Cybersecurity Awareness Month: Meet Sugey Ochoa, security partner
 October 12, 2026 •

October is National Cybersecurity Awareness Month, and the UCOP Information Security Team is helping our colleagues learn how to protect themselves at work and in their private lives.
Security partner profile: Sugey Ochoa
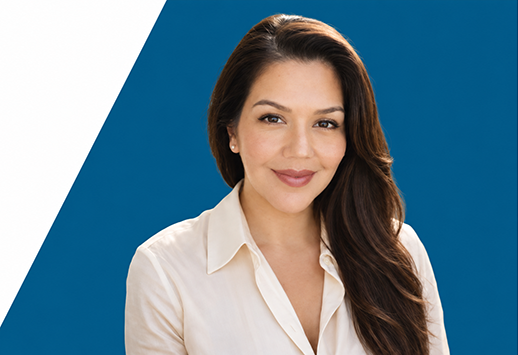
Sugey Ochoa, Assistant Director of Employee Services, UCPath
Sugey Ochoa’s career at UCPath spans more than 13 years. She has watched UCPath evolve from its legacy operations into the modern environment it is today, growing alongside it and becoming a trusted leader in the process. Today, she oversees five teams of supervisors and frontline staff who support employees with benefits, payroll, personal information and emerging security concerns. Her work is grounded in more than 20 years of leadership experience and an MBA in information systems, shaping a problem-solving approach rooted in people, process and technology.
Ochoa’s path into this work reflects her genuine interest in people and her ability to navigate complex, high-pressure situations with clarity and composure. “I enjoy interacting with people,” she explained. “Even though no one likes working under stress, I thrive in problem-solving environments.” She encourages her staff to approach each inquiry with patience, empathy and curiosity, reinforcing the importance of thoughtful engagement and consistent support for employees.
Since late 2023, UCPath has seen a significant rise in security-related incidents involving the use of artificial intelligence to gather public information, craft convincing phishing messages or impersonate employees. “Threat actors are getting very innovative,” she noted. “With AI, they can pull public information instantly. We have to stay vigilant.” UCPath’s visibility as part of a public institution makes awareness and proactive defense essential.
In response to these challenges, UCPath has strengthened internal processes, refined communication pathways and deepened collaboration with Information Security and operational partners. A key improvement was transforming direct deposit fraud monitoring from a manual review to an automated solution, significantly strengthening controls and improving response times. What began as an urgent effort to understand new attack patterns has evolved into a coordinated approach to protecting employee information.
Earlier this year, Ochoa presented this work at HEUG #ProtectYourPay, highlighting how collaboration and process enhancements have improved UCPath’s ability to respond quickly and effectively. “Now, when something happens, we do not have to stop and think about the next step,” she said. “We simply react.”
She urges employees to stay alert to unexpected messages, verify unusual requests and check URLs before clicking. She emphasizes the importance of recognizing subtle cues such as spelling errors, inconsistencies or urgent language that may signal an impersonation attempt. “If something does not feel right, flag it,” she said. “Ask questions; we are here to help. Do your research, verify everything, [and] remember that security is everyone’s responsibility.”
Looking ahead, Ochoa is focused on continuous improvement and thoughtful innovation. She sees artificial intelligence as both a risk and an opportunity, and she is exploring how UCPath might use internal AI tools to streamline processes while maintaining employee access. “We want to protect personal information,” she said, “but we also do not want to make it too challenging for employees to access their own data.”
Register for systemwide virtual cybersecurity events
Listings reflect Pacific Time. Select each event name for registration.
The Vibes Are Off: How to Safely Build Apps with AI Agents
Oct. 13, 2 – 3 p.m.
“Vibe coding,” using AI to write applications for you, is everywhere in the coding world. It promises to enable novice coders to create apps far beyond their skill level and to help all coders work more efficiently. But these AI tools usually prioritize functionality and speed over security. That can be great for little local scripts, but it’s much more problematic when used for work or research. Join UCLA Health’s Senior Mayhem Creator Michael Taggart on a journey to explore how vibe coding can be done responsibly and securely — and how it can go horribly wrong.
Mental Malware: Why the Human OS Keeps Getting Hacked
Oct. 15, 11 a.m. – 12 p.m.
Social engineering works because it targets what makes us human: our biases, cognitive shortcuts, emotions and deeply wired instinct to trust. Drawing on studies from the field of psychology, this session unpacks the brain’s architecture that enables manipulation to be disturbingly effective. Learn how generative AI is raising the stakes, making it harder than ever to differentiate what’s real and what’s not. You’ll leave with a deeper understanding of the psychology behind deception — and how to push back.
From Extortion to Espionage: The Frontline Threat Landscape for Higher Education
Oct. 15, 12 – 1 p.m.
Higher education institutions are prime targets for cyber threats ranging from lucrative ransomware schemes to sophisticated state-sponsored espionage. Join Jeremy Rosado, senior intelligence analyst with the Google Threat Intelligence Group, for an insider’s look into the evolving threat landscape confronting colleges and universities.
Should I Put That Into ChatGPT? Protecting UC Data When Using AI
Oct. 20, 10 – 11 a.m.
A conversation featuring UCSF Data Security Compliance Director Mary Morshed.
AI and Privacy
Oct. 21, 12 – 1 p.m.
How does rapid AI adoption intersect with modern privacy laws? Join Goodwin Associate Reema Moussa for a focused, one-hour session on protecting user data, staying compliant and mitigating legal risk in the age of AI.
AI, Deepfakes & Social Engineering
Oct. 28, 10 – 11 a.m.
This UCSF-sponsored conversation will feature Ben Syn, director of University and Career Education at KnowBe4.
Public Interest Cybersecurity: How Cal Researchers Defend Nonprofits, Schools and Cities from Digital Threats
Oct. 29, 11 a.m. – 12 p.m.
Who gets left behind when federal resources focus only on “national security threats”? Join this talk by Sarah Powazek, director of public-interest cybersecurity at the UC Berkeley Center for Long-Term Cybersecurity, to learn how Cal researchers are shaping the national conversation on “critical infrastructure.” Sarah will share more about cutting-edge survey research on nonprofits and international coalition-building efforts to provide a safety net of digital defenses for all organizations, regardless of their technology budget size. She will also highlight key market failures the team is investigating, innovative solutions such as cybersecurity clinics and student/regional SOCs, and other ways academia, industry, government and nonprofits are joining forces to provide defenses against rapidly growing digital threats.
ClickFix: Turning User Trust Into Code Execution
Oct. 29, 2 – 3 p.m.
What is the “ClickFix” compromise? Join us for a cybersecurity presentation led by UC Irvine’s cybersecurity club, Cyber@UCI, exploring ClickFix, a social engineering technique that tricks users into performing actions that can ultimately compromise their devices. During this interactive demo, we’ll show what ClickFix is, why it’s malicious and the warning signs you need to recognize. We’ll also cover practical defenses and simple steps you can take to stop an attack before it becomes a security incident. Know hackers’ tricks, and you’ll nix the ClickFix!
Additional cybersecurity resources
- Information Security website
- Report an Incident or Vulnerability
- UCOP Unit Information Security Lead Directory
- UCOP Records Management
Tags: cybersecurity, Cybersecurity Awareness Month, Sugey Ochoa


